WordPress Staging Environment: Because Testing in Production is a Dangerous Game
Why Every WordPress Site Owner Needs a Safe Testing Space
A WordPress staging environment is a private copy of your live website where you can safely test updates and design changes before they go live. It is a practice room where mistakes do not cost you customers or data.
Quick Summary:
- What it is: An isolated clone of your live site on a separate URL.
- Why you need it: To test plugins, themes, and PHP upgrades without risking uptime.
- How to create one: Use hosting tools, plugins like WP Staging, or manual subdomains.
- Key benefit: Catching fatal errors and layout shifts before the public sees them.
- Critical rule: Always block search engines from indexing your staging site.
Updating plugins directly on a live site is risky. A simple conflict can cause the “White Screen of Death” (WSoD), leading to lost sales. Staging environments provide a consequence-free space to spot these problems while they are still harmless.
As Kevin Gallagher, founder of wpOncall, I have managed thousands of WordPress sites. The difference between a stable site and a crisis is usually the habit of testing in staging first. Below, I will show you how to set up and use a staging environment effectively.
WordPress staging environment word roundup:
What is a WordPress Staging Environment and Why Do You Need One?
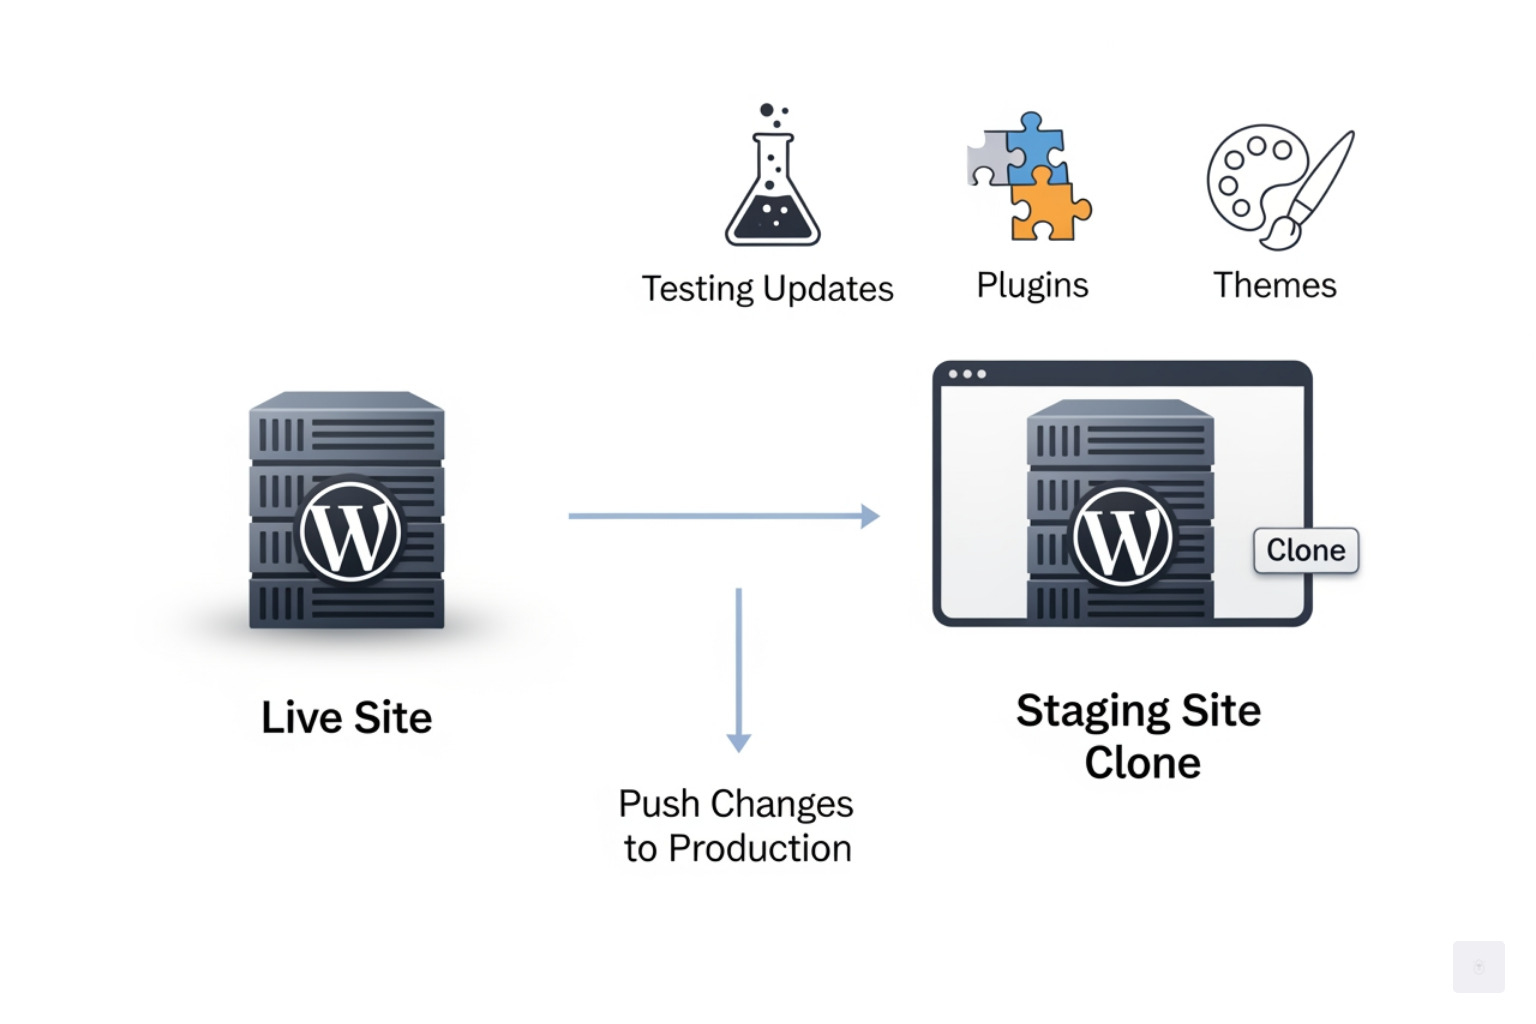
A WordPress staging environment is a private replica of your live website (often called production). It functions as a sandbox where you can change code, update plugins, and experiment with settings without visitors seeing the impact. Your live site serves customers. Your staging site lives on a hidden URL (for example, staging.yoursite.com or yoursite.com/staging) and exists for one purpose: to validate changes before you risk revenue, rankings, or reputation.
WordPress is flexible because it is modular. Themes, plugins, and custom code can be mixed and matched. That same flexibility creates risk. A single update can change PHP requirements, introduce a JavaScript conflict, or alter CSS in a way that breaks layout on mobile.
The real-world cost of downtime
Downtime is not just an inconvenience. It can be measured in lost sales, increased support load, and damaged trust. Even if you have a small brochure site, a broken contact form can quietly kill leads for days.
Common production failures that staging prevents include:
- Plugin conflicts: Example: you update a caching plugin and your checkout page stops loading because a script is minified incorrectly. On staging, you can identify the exact setting that caused the break and exclude that script before pushing live.
- Theme and block editor changes: Example: you switch typography or spacing and a button falls below the fold on mobile, reducing conversions. Staging lets you review the pages that drive revenue before shipping.
- Core updates: Example: a major WordPress release changes how scripts are enqueued or how blocks render. Staging lets you validate the front-end output and spot PHP warnings early.
- Performance tuning: Example: enabling object caching or changing your caching layer improves speed but causes stale content on dynamic pages. You can test caching exclusions in staging and compare results using PageSpeed Insights.
- Debugging and logging: Staging gives you a safe place to enable WP_DEBUG and detailed logging, reproduce a reported bug, and confirm the fix without exposing errors to the public.
- PHP upgrades: Example: moving from PHP 8.0 to 8.2 triggers deprecation warnings or fatal errors in older plugins. Staging is the safest way to validate compatibility and plan replacements.
What you should test on staging (a practical checklist)
Treat staging like a final rehearsal. Use a written script so you test the same things every time. Below is a more complete list than most site owners use, with concrete examples of what to click and what to verify.
Site-wide basics
- Homepage: loads without layout shifts, hero images display correctly, and key CTAs are visible on mobile.
- Navigation: open the menu on desktop and mobile, click through top-level items, test dropdown hover and tap behavior.
- Search: run a few queries that should return results (brand name, product category, a common blog topic).
- 404 and redirects: confirm your custom 404 page renders and that important legacy URLs still redirect correctly.
Forms and lead capture
- Submit the primary contact form with a real email address you control.
- Confirm validation messages display correctly.
- Confirm the submission is stored (if you use database storage) and that an email notification is generated.
- If you use reCAPTCHA or similar, confirm it still loads and does not break the submit action.
Ecommerce and transactions (if applicable)
- Add an item to cart, change quantities, apply a coupon, and proceed to checkout.
- Confirm taxes and shipping calculate correctly.
- Run a full checkout using your payment processor sandbox mode.
- Confirm order confirmation pages render correctly and that transactional emails are generated (logged, not sent to real customers).
Member and account flows (if applicable)
- Register a new user (or create one in admin), log in, log out.
- Test password reset.
- Confirm protected content remains protected and does not leak to logged-out users.
Content and editing
- Create a draft post, preview it, and ensure the editor is stable.
- Test any custom blocks or shortcodes.
- Confirm featured images and galleries render.
Performance and stability checks
- Compare PageSpeed Insights results before and after major changes.
- Browse key pages with the browser console open and look for JavaScript errors.
- Check PHP error logs (or your host logs) for warnings after updates.
If you adopt staging as a habit, most WordPress emergencies become routine maintenance. The goal is not perfection. The goal is to catch the expensive, public failures before your audience does.
Where helpful, compare results using Lighthouse documentation and metrics definitions so your team speaks the same language.
The Technical Differences: Staging vs. Development vs. Production
Professional workflows usually follow a path: Development -> Staging -> Production. Each environment exists to reduce risk and make changes repeatable.
| Feature | Development (Local) | Staging Environment | Production (Live) |
|---|---|---|---|
| Location | Your computer | Private web server | Public web server |
| Visibility | Only you | Private | Public |
| Purpose | Coding and experiments | Final testing and QA | Serving real users |
| URL | localhost | staging.yoursite.com | yoursite.com |
| Database | Dummy or masked data | Clone of live data | Real-time data |
Development: fastest iteration, lowest realism
Local development is where you change code quickly. It is ideal for:
- Building a new template or block.
- Trying a new plugin.
- Writing custom functions.
Its downside is realism. Your laptop is not your server. PHP versions, server caching, and file permissions often differ. Something that works locally can fail on a real host.
Staging: realism without the public risk
Staging should mirror production as closely as possible:
- Same PHP version
- Same WordPress version
- Same active theme and plugins
- Similar caching layers and server configuration
Staging is where you do QA: click through checkout, confirm forms send, confirm performance changes are acceptable, and confirm nothing breaks on mobile.
Production: the only place that matters to customers
Production is where real orders, signups, and form submissions happen. Because production data changes minute by minute, it creates a key WordPress challenge: you cannot safely overwrite your production database with a staging database without risking data loss.
Database serialization and why URL changes break sites
A major hurdle in staging is database serialization. WordPress stores some values as serialized arrays, which include string length metadata. If you manually change URLs in a raw SQL export (for example, changing https://yoursite.com to https://staging.yoursite.com) you can corrupt those serialized values. Symptoms range from broken widgets to complete failure, sometimes showing as the “White Screen of Death.”
Safer options include:
- WP-CLI search-replace (handles serialization correctly): https://developer.wordpress.org/cli/commands/search-replace/
- Purpose-built migration tooling that understands WordPress data formats
Environment flags that prevent staging accidents
WordPress supports the WP_ENVIRONMENT_TYPE constant in wp-config.php. Setting it to staging helps well-behaved plugins and custom code adjust behavior (for example, disabling integrations or turning on logging).
Add this to wp-config.php on staging:
define( 'WP_ENVIRONMENT_TYPE', 'staging' );
Reference: https://wordpress.org/documentation/article/editing-wp-config-php/
Data privacy: staging often contains real customer data
If you clone production to staging, you may also clone:
- Customer emails
- Order history
- Form submissions
- User accounts
That means staging should be treated as sensitive:
- Restrict access with authentication
- Use HTTPS
- Limit user accounts
- Avoid sharing staging URLs publicly
If you need to let stakeholders review staging, consider using masked data or restricting access by IP where possible.
How to Create a WordPress Staging Environment: 4 Proven Methods
There are several correct ways to create a WordPress staging environment. The best choice depends on your hosting, your technical comfort, and how often you deploy changes.
Method 1: Hosting provider one-click staging (recommended)
Many managed WordPress hosts provide built-in staging. This is often the most reliable method because it mirrors your live server’s PHP version, memory limits, and caching layers.
Typical workflow
- Log in to your hosting dashboard and find the Staging section.
- Click “Create Staging” and wait for cloning to finish.
- Log in to the staging WordPress admin and go to Settings -> Reading and check “Discourage search engines from indexing this site.”
- Confirm the staging site is protected (password or other access controls).
- Switch payment gateways to sandbox mode and disable any automated email sending.
What to verify after the clone
- The staging URL loads over HTTPS.
- The wp-admin login works and you can reach the dashboard.
- Media library images load correctly.
- Permalinks work (if not, re-save Settings -> Permalinks).
Method 2: Staging plugins
If your host does not offer staging, a staging plugin can clone your site into a subdirectory and rewrite URLs.
Pros
- Easier than manual cloning
- Useful on basic shared hosting
Limitations
- Cloning runs on your live server, so large sites can time out or slow down production during the clone
- Storage requirements can nearly double
- Some plugins struggle with very large databases or multisite
Best practices if you use a plugin approach
- Clone during low-traffic hours
- Exclude cache directories and backup directories from the copy if possible
- Consider excluding uploads for very large media libraries (knowing images may appear missing on staging)
Method 3: Manual staging on a subdomain (most control)
This method offers full control but requires comfort with DNS, SFTP, and database tools.
Step-by-step overview
Create a subdomain
- Create staging.yoursite.com in your DNS.
- Point it to a new directory on your server (for example, /public_html/staging).
Copy WordPress files
- Copy all WordPress files from production into the staging directory.
- Exclude unnecessary cache and backup folders if you know they will be regenerated.
Clone the database
- Create a new database and database user for staging.
- Export the production database and import it into the staging database.
Update wp-config.php
- Point staging to the staging database name, user, and password.
- Set the environment type:
define( 'WP_ENVIRONMENT_TYPE', 'staging' );
Update URLs safely (do not edit SQL by hand)
- Use WP-CLI search-replace so serialization stays intact: https://developer.wordpress.org/cli/commands/search-replace/
- Example concept: replace https://yoursite.com with https://staging.yoursite.com
Harden staging access
- Add password protection.
- Ensure robots are blocked (noindex).
- If possible, restrict access by IP.
Common manual-staging gotchas
- Mixed-content warnings if staging uses HTTPS but URLs still reference HTTP assets.
- Hard-coded URLs inside theme options or page builder settings.
- Caching layers that need to be cleared or disabled for accurate testing.
Method 4: Local development -> staging workflow
Developers often build locally, then deploy to a staging server for review. This is especially useful when:
- You are changing theme code or writing custom plugins.
- You want repeatable deployments.
- You need rollback capability.
A practical workflow looks like:
- Create a local copy for development.
- Commit changes and deploy them to staging.
- Run a test script on staging.
- Deploy the same changes to production after approval.
Choosing the right method
- If your host provides staging, use it.
- If you need a quick staging setup on shared hosting, a staging plugin is often the simplest.
- If you need maximum control, use a manual subdomain.
- If you ship code regularly, adopt a local-to-staging workflow so changes are repeatable.
No matter which method you choose, the quality of the staging environment is defined by how closely it matches production and how consistently you test before pushing changes.
Deploying Changes: How to Push from Staging to Live Production
Moving changes from staging to production is the highest-risk moment in a WordPress workflow. A WordPress site consists of files (themes, plugins, uploads) and the database (content, settings, users, orders). The safest deployment approach depends on what changed.
The core rule: treat the production database as the source of truth
Production data changes constantly. New form submissions, comments, orders, and user registrations happen while you test on staging. If you push a full staging database to production, you can overwrite that new production data.
This is the “database dilemma” and it is why many professional workflows default to pushing files only and applying database changes carefully.
The safest deployment strategy (step-by-step)
Freeze the plan
- Write down what you are deploying: plugin updates, theme changes, new pages, settings changes.
- Decide whether each item is a file change, a database change, or both.
Take a fresh production backup
- Take a manual backup immediately before deployment.
- Verify you can access the backup and that it includes both files and database.
Deploy low-risk changes first
- Push files that you know are safe (for example, child theme CSS updates).
- Avoid pushing database changes unless necessary.
Handle database changes selectively
- If you created new pages or posts on staging, use WordPress export/import to move just content when possible.
- If a plugin update changed settings, re-apply the settings manually on production so you do not overwrite unrelated tables.
WordPress export documentation: https://wordpress.org/documentation/article/tools-export-screen/
Validate production in a clean session
- Use an incognito window.
- Test the top user flows: navigation, forms, checkout, search.
Clear caches in the right order
- Purge WordPress cache (if applicable).
- Purge server cache.
- Purge CDN cache.
Monitor logs and uptime
- Check PHP error logs after deployment.
- Watch for 404 spikes or JavaScript errors.
Practical examples: what to push and what not to push
Example A: You updated three plugins on staging and everything works
- Usually safest approach: repeat the same plugin updates directly on production during low-traffic hours.
- Why: it avoids database overwrites and keeps production data intact.
Example B: You changed CSS and a few template files
- Push: theme files (or child theme files) only.
- Do not push: database.
- Validate: homepage, key landing pages, mobile menu.
Example C: You built a new landing page in the block editor
- Use WordPress export/import for that page or recreate it on production.
- If the page uses reusable blocks or patterns, export those too.
WooCommerce guidance
Ecommerce sites require extra discipline.
- Never do a full database push from staging to production.
- Test plugin and theme updates on staging.
- Apply updates on production in a maintenance window.
- Use sandbox mode on staging for payments.
WooCommerce has a sandbox/testing concept via payment gateways and test modes; always rely on the gateway provider documentation for test card numbers and sandbox keys.
Post-deployment checklist
- Permalinks: go to Settings -> Permalinks and click Save to flush rewrite rules if anything seems off.
- Forms: submit the primary form end-to-end.
- Checkout: run a test order (if applicable) using a test gateway mode.
- Search: confirm onsite search still returns results.
- Error logs: check for new warnings or fatal errors.
- Noindex check: confirm production is not accidentally set to discourage indexing.
The goal is consistent, repeatable deployments that minimize the chance of customer-visible failures.
Critical Mistakes to Avoid in Your WordPress Staging Environment
Staging environments reduce risk, but only if they are configured safely. The mistakes below are responsible for most staging-related SEO problems, security incidents, and confusing customer communications.
1. Allowing search engine indexing
If staging is crawlable, it can create duplicate content issues and split ranking signals. It can also expose content you intended to keep private.
Minimum protections
- In WordPress admin: Settings -> Reading -> enable “Discourage search engines from indexing this site.”
- Add authentication (basic auth or other access control) so the public cannot browse staging.
- Ensure staging pages return a noindex directive.
Google documentation on robots meta tags: https://developers.google.com/search/docs/crawling-indexing/robots-meta-tag
Important warning: The most common SEO mistake is pushing a noindex setting from staging to production. After any deployment, confirm production indexing settings.
2. Testing only the homepage
Many failures do not show on the homepage:
- a broken checkout step
- a membership login loop
- a form that fails silently
- a mobile menu that does not open
Fix: maintain a written test script that includes your money pages: contact, booking, checkout, top landing pages, and key blog templates.
3. Environment mismatches
If staging runs PHP 8.2 while production runs PHP 8.0, your staging test is not reliable. The same goes for memory limits, caching layers, and server modules.
What to match
- PHP version
- WordPress version
- Database version (where possible)
- Server caching and CDN behavior (as much as feasible)
You can compare environments by checking your host settings and, if needed, creating a temporary phpinfo file (then deleting it).
4. Sending real emails from staging
Staging sites often contain real customer data. If a cron job runs and emails send, customers can receive confusing test notifications.
Safer options
- Use an email logging approach so mail is captured, not delivered.
- Use a mail trapping service in staging.
- Disable scheduled tasks if appropriate.
WordPress cron overview: https://developer.wordpress.org/plugins/cron/
5. Using live payment gateways
Always swap API keys to sandbox mode on staging. If you forget, you can charge real cards or create real subscriptions during testing.
Checklist for staging payments
- Confirm gateway is in test mode.
- Confirm webhook endpoints (if used) do not point to production processing.
- Use only test card numbers from your payment provider.
6. Skipping performance checks
A change can “work” and still hurt conversions by slowing down the site or increasing layout instability.
How to test
- Run PageSpeed Insights before and after major changes: https://pagespeed.web.dev/
- Focus on LCP and CLS.
- Check for new render-blocking scripts.
7. Never refreshing staging
An old staging copy is a false sense of safety. It may not contain recent production content, new plugin versions, or current theme state.
Best practice
- Re-clone staging from production before each new round of work.
- Delete staging environments that are not in active use to reduce attack surface.
8. Leaving staging publicly accessible
Even if staging is noindex, it can still be discovered and attacked. Staging sites are often less monitored and may run outdated plugins.
Fix
- Require login (basic auth or SSO).
- Use strong passwords and limit admin accounts.
- Keep staging updated, or shut it down when not needed.
Treat staging as production-grade infrastructure with restricted access, not a throwaway copy.
Frequently Asked Questions
Will a staging site affect my SEO?
Not if you block indexing and restrict access. The biggest SEO risk is accidentally pushing a “noindex” configuration to production after testing.
Helpful references:
- Robots meta tags: https://developers.google.com/search/docs/crawling-indexing/robots-meta-tag
- Robots.txt basics: https://developers.google.com/search/docs/crawling-indexing/robots/intro
How do I keep staging synchronized?
In most workflows, synchronization is one-way: production to staging. You refresh staging by cloning production again at the start of each project.
If you must keep staging partially updated while work is in progress, document exactly what changed in production (new plugins, new settings, new pages) so your staging tests remain realistic.
Is it safe to delete my staging site?
Yes. In many cases it is a security best practice to delete staging when not in use. A forgotten staging environment is a common attack target.
How do I prevent staging from sending notifications?
Use an approach that captures mail rather than sending it. Options include mail logging in WordPress or routing mail through a trapping service in staging. Also review scheduled tasks so automated emails do not fire unexpectedly.
How much disk space does staging use?
Often close to the same as production because it includes a full copy of your WordPress files and database. Media libraries can be the largest component. If disk space is limited, consider excluding uploads when cloning (with the tradeoff that images may not display on staging).
Can I use staging for Multisite?
Yes, but it is more complex because multisite stores network URLs and domain mapping in the database. Prefer a staging approach that explicitly supports multisite and test carefully, especially if you use mapped domains.
Do I need separate user accounts on staging?
It is recommended. Use the minimum number of admin accounts, restrict access to stakeholders, and avoid sharing production credentials widely. If staging includes real user data, consider limiting who can access it.
How often should I use staging?
Use staging for any change that could affect availability, revenue, security, or SEO. Examples include plugin updates, theme updates, PHP upgrades, caching changes, and any checkout or form modifications.
Conclusion
A WordPress staging environment is the best investment for website stability. It turns stressful updates into a controlled workflow, protecting your brand, SEO, and revenue.
In an era of high security and performance standards, guessing is not an option. Whether you use hosting tools or plugins, the goal is to ensure every change is a step forward.
At wpOncall, we provide peace of mind for WordPress owners. We handle technical heavy lifting—including staging setups and migrations—so you can focus on growth. Ready to professionalize your workflow? More info about WordPress help services is just a click away. Let us help you build a more resilient website today.