wordpress set ssl certificate

Secure Your Site Today with This Easy WordPress SSL Certificate Guide

Why Every WordPress Site Owner Needs to Set an SSL Certificate

WordPress set SSL certificate is one of the most important steps you can take to protect your site and your visitors. Here is a quick overview of how to do it:

  1. Get an SSL certificate – most hosting providers offer free SSL through Let’s Encrypt
  2. Activate SSL via your hosting control panel (cPanel, Plesk, or hosting dashboard)
  3. Update your WordPress URLs from http:// to https:// in Settings > General
  4. Update database URLs using a plugin like Better Search Replace
  5. Force HTTPS redirects by editing your .htaccess file or Nginx config
  6. Fix mixed content warnings so all page resources load securely
  7. Verify the installation by checking for the padlock icon in your browser

Without SSL, browsers like Chrome flag your site as “Not Secure.” That warning drives visitors away and hurts your search rankings. Google has used HTTPS as a ranking signal since 2014, and regulations like GDPR make encrypted connections a legal requirement for many sites.

The good news: SSL is no longer hard or expensive to set up. Free certificates from Let’s Encrypt work just as well as paid ones for most WordPress sites.

I’m Kevin Gallagher, and over my 15+ years building and maintaining WordPress websites – including helping clients properly wordpress set ssl certificate across hundreds of sites – I’ve seen how a missing or misconfigured SSL certificate can quietly damage a business. Let’s walk through everything you need to know to get it right.

WordPress set ssl certificate terms made easy:

Understanding SSL and Why Your WordPress Site Needs It

When we talk about a wordpress set ssl certificate process, we are moving your site from HTTP to the secure HTTPS protocol. SSL (Secure Sockets Layer), now technically TLS (Transport Layer Security), creates an encrypted connection between a visitor’s browser and your server.

Without SSL, data like login credentials, contact form submissions, search queries, and account cookies can be sent in plain text, making it vulnerable to interception on insecure networks. With an SSL certificate, that data is encrypted in transit. This is vital for all sites, not just e-commerce, because WordPress handles authentication cookies, admin sessions, password resets, and user-submitted data by default.

Beyond security, there are three major reasons to prioritize SSL:

  1. SEO Power: Google has used HTTPS as a ranking signal since 2014. While it is not the only ranking factor, HTTPS is now a baseline trust signal for search engines and users alike.
  2. User Trust: Browsers flag HTTP sites as “Not Secure,” especially on login pages and forms. A padlock icon reassures users that their connection is private and that the site owner has taken basic security steps.
  3. Compliance: Regulations like GDPR and PCI DSS effectively require encrypted transport when personal or payment-related data is being transmitted.
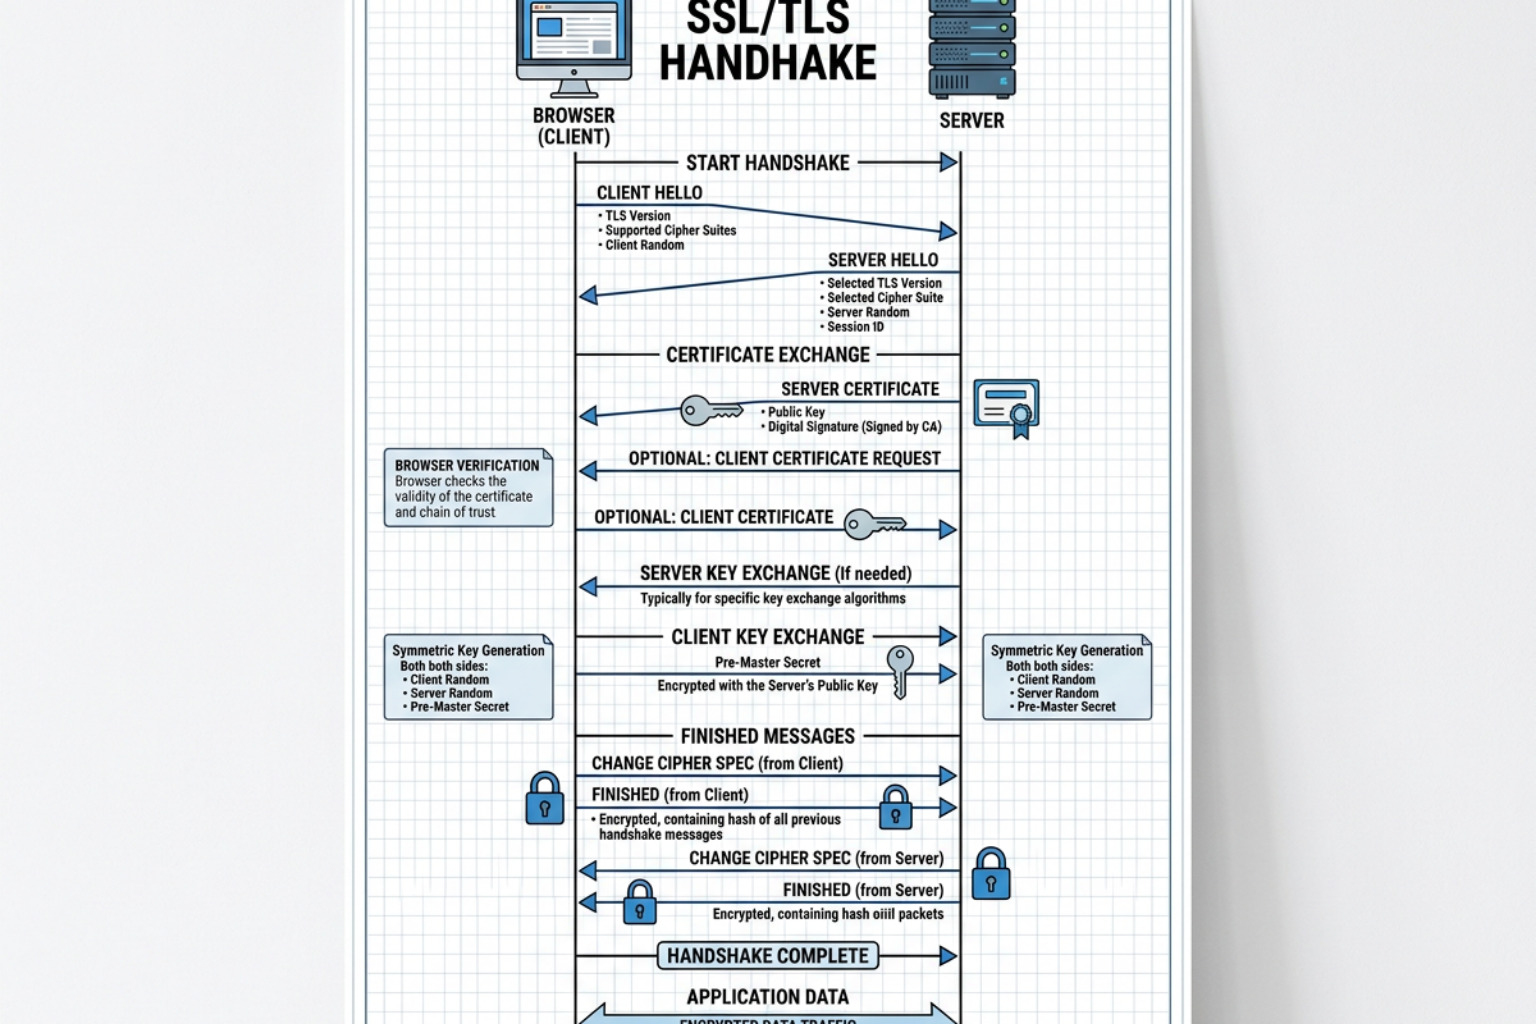
SSL Handshake Process Diagram - wordpress set ssl certificate

Here is a simple example. If a visitor logs in to http://yourdomain.com/wp-admin, the username and password exchange is far more exposed than if the same login happens over HTTPS. The same applies to contact forms, newsletter signup forms, and WooCommerce checkout pages. Even if you do not think your site handles sensitive data, WordPress itself does.

A modern HTTPS connection also helps protect against tampering. Without encryption, an attacker on the network may be able to inject malicious code, ads, or redirects into a page before it reaches the visitor. That is one reason HTTPS is considered essential even for blogs and brochure sites.

If you see “Not Secure” in your browser, our unlock HTTPS your easy WordPress SSL guide can help.

How SSL Actually Works in Practice

When a browser visits your site over HTTPS, it checks the certificate presented by your server. That certificate confirms that the server controls the domain name and enables the browser and server to negotiate an encrypted session. In a normal setup, the process looks like this:

  1. The visitor enters your domain in the browser.
  2. The browser connects to your server and requests a secure session.
  3. Your server presents the SSL certificate.
  4. The browser verifies that the certificate is valid, current, and issued for the correct domain.
  5. A secure encrypted session is established.
  6. The page loads over HTTPS, and the browser displays the padlock.

If any part of that chain fails, visitors may see certificate warnings, trust errors, or blocked resources.

Free vs. Paid SSL Certificates

For most WordPress sites, a free certificate is sufficient.

  • Free Certificates (Let’s Encrypt): These provide standard Domain Validation (DV) and the same encryption strength as paid options. Most hosts automate their 90-day renewal cycle.
  • Paid Certificates (OV/EV): These involve deeper organizational checks. They are often used by large enterprises for internal policy reasons rather than stronger encryption.
  • Wildcard Certificates: Useful if you need to secure multiple subdomains (e.g., shop.example.com).

A common misunderstanding is that paid certificates somehow encrypt data more strongly. In most practical WordPress use cases, that is not true. The strength of the encryption depends on modern TLS configuration, supported cipher suites, server setup, and certificate validity, not whether the certificate was free or expensive.

When You Might Need More Than a Basic Certificate

A standard DV certificate is enough for most site owners. Still, some situations call for a more specific setup:

  • You run several subdomains and want one certificate to cover all of them.
  • You use a load balancer or reverse proxy in front of WordPress.
  • You manage a multisite network with mapped domains.
  • You need separate certificates for staging and production environments.
  • Your host requires manual certificate installation rather than one-click issuance.

In short, not having SSL is a major risk; using a free Let’s Encrypt certificate is a perfectly valid solution for the vast majority of site owners.

Preparing Your Server to Set SSL Certificate on WordPress

Before you wordpress set ssl certificate, ensure your environment is ready. Most modern hosts support SNI, so a dedicated IP is rarely needed. Ensure your DNS (A records) points correctly to your server, as certificate authorities must verify domain control before issuance.
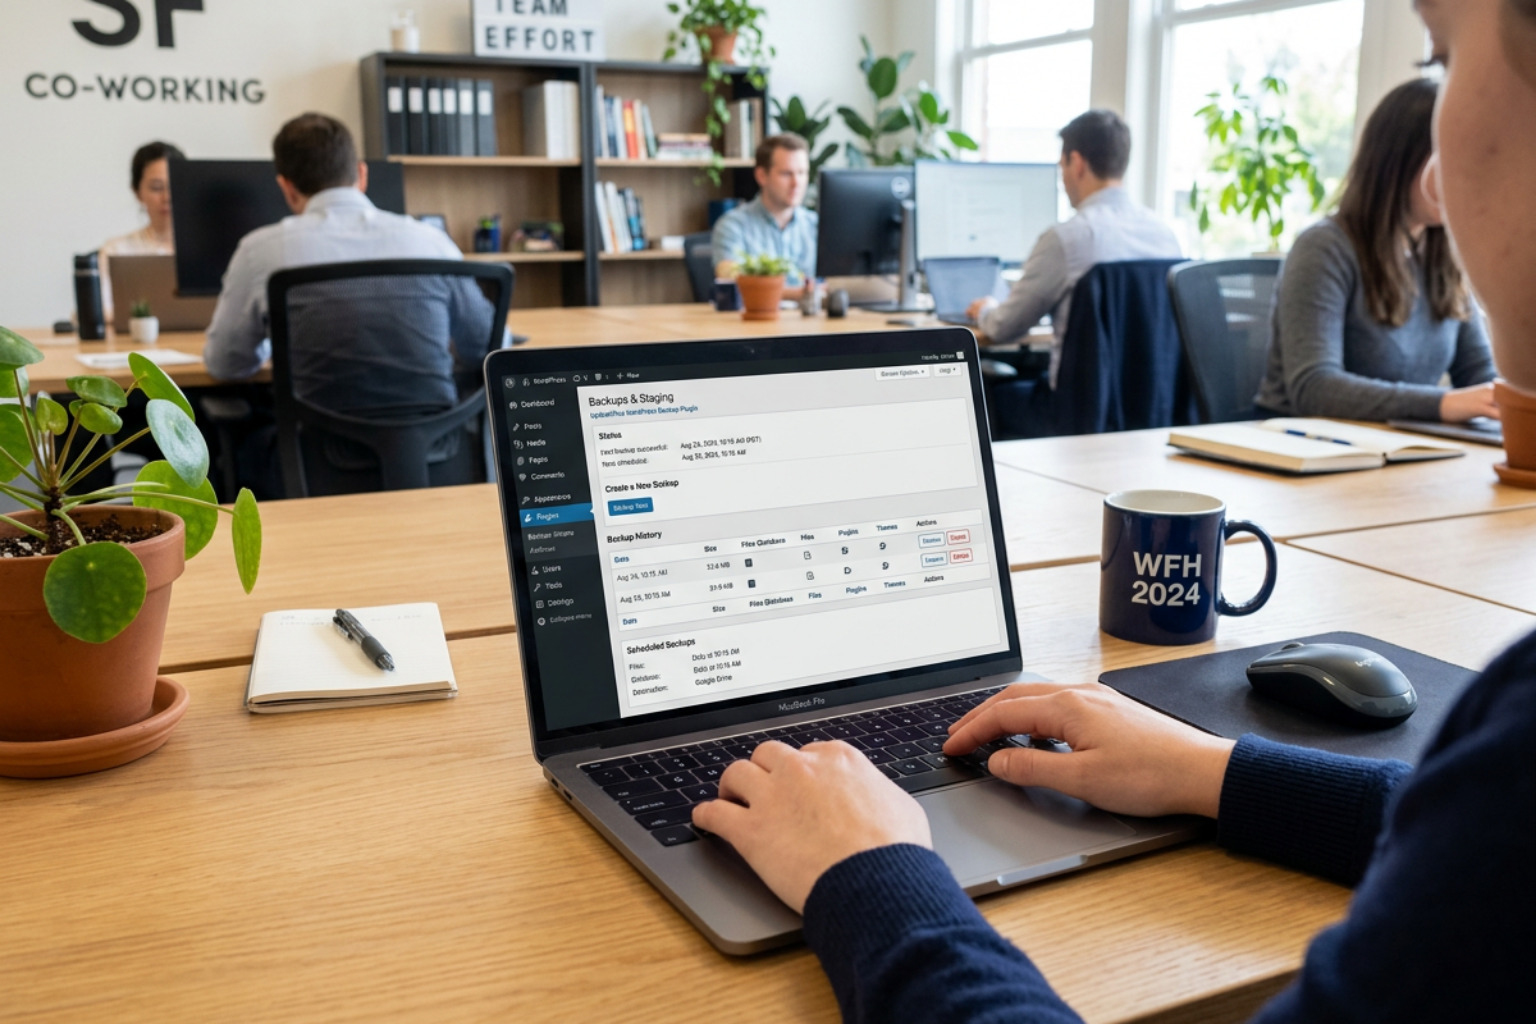
WordPress Backup Interface - wordpress set ssl certificate

Essential Pre-Installation Backup Procedures

Always backup your site before changing SSL settings. Incorrect URL changes can cause redirect loops, broken media links, admin login issues, or plugin conflicts.

  1. Database Export: Use WP Migrate or your hosting panel to export a full SQL file.
  2. File Backup: Copy your wp-config.php and .htaccess files.
  3. Staging: If possible, test the Changing the Site URL process on a staging site first.

For technical details, see our WordPress SSL certificate installation brief. Schedule these changes during low-traffic periods to minimize the impact of any temporary configuration issues.

Pre-Flight Checklist Before You Install

Before you request or activate the certificate, check the following:

  • DNS is correct: Your domain and www version should point to the correct server IP.
  • Hosting access is available: Make sure you can log into cPanel, Plesk, your managed host dashboard, or your server via SSH.
  • CDN and proxy settings are documented: If you use Cloudflare or another proxy, know whether it is handling SSL at the edge, at the origin, or both.
  • Existing redirects are reviewed: Old redirect rules in .htaccess, Nginx config, or a redirection plugin can interfere with HTTPS rules.
  • Theme and plugin updates are stable: If your site is already in a fragile state, fix that first before layering in SSL changes.

Common Hosting Scenarios

The exact preparation depends on where WordPress is hosted:

  • Shared hosting: SSL is usually enabled from a dashboard and may renew automatically.
  • Managed WordPress hosting: The platform often provisions certificates automatically, but you still need to confirm WordPress URLs and redirects.
  • VPS or cloud server: You are responsible for certificate issuance, web server config, renewal jobs, and validation.
  • Local or staging site: Self-signed certificates may be fine for testing, but they should not be used on production.

Why Backups Matter So Much Here

A simple URL mistake can lock you out of the WordPress dashboard or cause endless redirects between HTTP and HTTPS. Having a database backup means you can restore the old siteurl and home values quickly. Keeping copies of .htaccess and wp-config.php also lets you revert forced redirect rules or SSL constants if needed.

As a practical example, if you change your WordPress Address to https:// before the certificate is active on the server, the admin area may become inaccessible. A backup and file manager access can save a lot of time in that situation.

Step-by-Step Guide to Install and WordPress Set SSL Certificate

There are three primary ways to handle a wordpress set ssl certificate task:

Method Ease of Use Best For
Hosting Panel Very Easy Beginners and Most Businesses
Plugin Easy Users on restrictive hosts
Certbot (SSH) Advanced VPS owners and Developers

Most reputable hosts offer “One-Click Let’s Encrypt.” In cPanel, look for SSL/TLS Status and click “Run AutoSSL.” This is the core of any WordPress hosting free SSL guide. Managed WordPress hosting with SSL certificate plans often handle this via a simple dashboard toggle.

A typical cPanel workflow looks like this:

  1. Log in to cPanel.
  2. Open SSL/TLS Status or your host’s SSL section.
  3. Select the domain and www subdomain if both are in use.
  4. Click Run AutoSSL or enable Let’s Encrypt.
  5. Wait for the certificate to be issued and installed.
  6. Visit both http:// and https:// versions of the domain to verify that HTTPS is working.

In Plesk or custom hosting dashboards, the steps are similar even if the menu names differ. Look for terms such as “Security,” “SSL,” “Certificates,” or “Let’s Encrypt.” If the dashboard offers a checkbox for redirecting all traffic to HTTPS, enable it only after verifying the certificate installed successfully.

Method 2: Manual Installation via Certbot

If you manage a VPS (Ubuntu/Nginx/Apache), use Certbot to generate SSL certificate WordPress files:

  1. Install Certbot: sudo apt install certbot python3-certbot-apache.
  2. Run: sudo certbot --apache -d yourdomain.com.
  3. Verify auto-renewal: sudo certbot renew --dry-run.

If you use Nginx instead of Apache, the package and command may differ slightly. The general process is:

  1. Update the server packages.
  2. Install Certbot and the correct web server plugin.
  3. Request a certificate for the domain and any required subdomains.
  4. Allow Certbot to update the web server config if appropriate.
  5. Test the web server config.
  6. Reload Apache or Nginx.
  7. Confirm renewal is scheduled through cron or systemd timers.

Manual installation gives you more control, but it also creates more ways to misconfigure the site. For example, if your server block still listens on port 80 without a proper redirect, some users may continue to access the insecure version. If the certificate covers only yourdomain.com but not www.yourdomain.com, one version of the site may still trigger warnings.

Method 3: Using a Plugin

Plugins like Really Simple SSL can help WordPress recognize HTTPS if your host has limited tools. However, server-level configuration is always faster and more reliable. Use plugins primarily to fix admin URL issues or minor mixed content problems after the certificate is already active on the server.

A plugin-based workflow usually looks like this:

  1. Activate SSL at the hosting or server level first.
  2. Install the plugin.
  3. Let it detect HTTPS.
  4. Update URLs or enable recommended fixes.
  5. Test the front end, admin area, and forms.

Be careful not to rely on a plugin to solve a missing certificate. A plugin cannot create a trusted HTTPS connection if the server itself is not presenting a valid certificate.

Which Method Should You Choose?

For most site owners, the best option is the hosting control panel because it is quick, supported by the host, and usually tied to automatic renewals. Certbot is ideal for developers or system administrators who control their own server. Plugins are a useful support layer, not the foundation of the setup.

A good rule is simple: install the certificate at the server level first, then update WordPress, then force redirects, then fix mixed content.

Post-Installation: Configuring WordPress for HTTPS

Once the certificate is installed, you must tell WordPress to use it. Go to Settings > General and change both the “WordPress Address” and “Site Address” from http:// to https://. This is a vital part of any SSL certificate update.

To secure the back end, add this to your wp-config.php: define('FORCE_SSL_ADMIN', true);

Fixing Mixed Content

Mixed content occurs when your database contains hardcoded http:// links to images, stylesheets, scripts, fonts, or iframe resources. Use the Better Search Replace plugin to search for http://yourdomain.com and replace it with https://yourdomain.com. This safely handles serialized data in your theme and widget settings.

A careful process looks like this:

  1. Run a dry search first to see how many URLs will be replaced.
  2. Confirm the exact domain format used in the database.
  3. Replace http://yourdomain.com with https://yourdomain.com.
  4. Clear all caches, including plugin, server, and CDN cache.
  5. Test key pages such as the homepage, blog posts, forms, checkout pages, and the WordPress admin.

For stubborn scripts, see our guide on how to fix not secure website WordPress.

Common mixed content sources include:

  • Theme files with hardcoded http:// asset paths
  • Old page builder content
  • Embedded images inside widgets or custom fields
  • External scripts that do not support HTTPS
  • Old media URLs inserted directly into posts years ago

Implementing Server-Level Redirects

Force all traffic to HTTPS using a 301 redirect. For Apache, add this to .htaccess:

RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]

For Nginx:

server {
 listen 80;
 server_name yourdomain.com;
 return 301 https://yourdomain.com$request_uri;
}

A 301 redirect tells browsers and search engines that the secure URL is the permanent version. That helps consolidate ranking signals and ensures users land on the HTTPS version even if they type the old address or follow an outdated link.

Additional Configuration Steps You Should Not Skip

After implementing, verify the padlock appears on all pages and update your external tools like Google Search Console to reflect the new HTTPS URLs.

You should also:

  1. Update your sitemap if it contains absolute URLs.
  2. Resubmit the HTTPS property in Google Search Console.
  3. Update analytics, ad platforms, and tracking tools if they still reference HTTP URLs.
  4. Check canonical tags and Open Graph tags for HTTPS consistency.
  5. Review robots.txt and any hardcoded internal links.

Testing Checklist After the Switch

Before considering the migration complete, test these items:

  • Homepage loads over HTTPS
  • Admin login works over HTTPS
  • No browser warnings appear on forms or checkout pages
  • Images, CSS, and JavaScript all load over HTTPS
  • Mobile and desktop versions behave normally
  • Redirect from HTTP to HTTPS works for both www and non-www

These checks catch the most common issues early, before search engines recrawl the site or visitors start reporting broken behavior.

Troubleshooting and Maintaining Your WordPress Set SSL Certificate

A wordpress set ssl certificate requires ongoing monitoring. Use Qualys SSL Labs to check for handshake errors, protocol weaknesses, incomplete certificate chains, and configuration gaps.

Common Issues and Solutions

  • Expired Certificates: Usually due to failed auto-renewal or DNS changes. Check your host’s SSL status.
  • Redirect Loops: Often caused by conflicting CDN (Cloudflare) settings. Ensure your CDN SSL mode matches your origin server.
  • Mixed Content: Use the browser console to identify specific assets still loading over HTTP.

If you are starting fresh, our guide from zero to secure mastering SSL certificate installation covers these basics.

Let us break down the most common problems in more detail.

1. Certificate Shows as Invalid

Possible causes include:

  • The certificate was issued only for the root domain, not the www version.
  • The certificate chain is incomplete.
  • The domain points to the wrong server.
  • The browser is seeing an old cached certificate.

What to do:

  1. Check which domain names are covered by the certificate.
  2. Confirm DNS is pointing to the intended server.
  3. Purge CDN cache if a proxy is in front of the site.
  4. Reissue the certificate if required.

2. Redirect Loop Between HTTP and HTTPS

This often happens when one layer forces HTTPS while another thinks the request is already secure or insecure. Common conflict points include:

  • .htaccess rules
  • Nginx server blocks
  • WordPress plugins
  • CDN SSL settings
  • Reverse proxy headers

What to do:

  1. Temporarily disable redirect plugins.
  2. Review .htaccess or Nginx rules for duplicate redirects.
  3. Check Cloudflare or proxy SSL mode.
  4. Verify WordPress Address and Site Address use https://.

3. Mixed Content Warnings Persist

Even after a database search-replace, some warnings remain because assets may be loaded dynamically from theme settings, inline scripts, or third-party services.

What to do:

  1. Open the browser developer console.
  2. Identify each blocked URL.
  3. Update the source in the theme, widget, plugin setting, or custom code.
  4. Replace or remove third-party resources that do not support HTTPS.

4. Auto-Renewal Fails

Let’s Encrypt certificates are short-lived by design, so automation matters.

Common reasons for failed renewal:

  • DNS records changed
  • Validation files are blocked
  • Cron jobs or timers are disabled
  • The web server config changed after issuance

What to do:

  1. Check your host’s SSL logs or Certbot logs.
  2. Run a dry renewal test if you manage the server.
  3. Confirm the domain still resolves correctly.
  4. Fix validation path or web server issues before the next expiration date.

Maintenance Best Practices

  1. Automate Renewals: Ensure Let’s Encrypt tasks are active.
  2. Hardening: Disable old protocols (TLS 1.0/1.1) in favor of TLS 1.2 and 1.3.
  3. Audit: Periodically check your site after host migrations or plugin updates to ensure the padlock remains intact. Monitoring your SSL setup is as important as monitoring your backups and uptime.

Ongoing Review Schedule

A practical maintenance routine looks like this:

  • Monthly: Confirm the site still redirects properly and loads without warnings.
  • Quarterly: Run an SSL test and review certificate expiration dates.
  • After major changes: Recheck HTTPS after migrations, CDN changes, theme changes, or domain updates.
  • Before peak sales periods: Test checkout, forms, and user account pages to avoid trust-breaking errors.

SSL is not a one-time task. It is part of regular WordPress maintenance, and a neglected certificate can quietly undo a lot of the trust your site has built.

Frequently Asked Questions about WordPress SSL

How do I check if my WordPress site already has SSL enabled?

The easiest way is to look at your browser’s address bar. If you see a padlock icon and the URL starts with https://, you have SSL. You can also use an online SSL Checker to see the technical details, such as the issuer and expiration date.

What should I do if SSL breaks my WordPress site or causes a redirect loop?

This usually happens because of a conflict between your server settings and a plugin (like Really Simple SSL) or a CDN (like Cloudflare). First, try to access your site via the IP address or disable your .htaccess redirect to regain access. Check your wp-config.php to ensure you haven’t hardcoded the wrong URL. If you’re using Cloudflare, ensure your SSL setting is set to “Full” or “Full (Strict)” rather than “Flexible.”

Can I use a free SSL certificate for an e-commerce store?

Absolutely. Let’s Encrypt certificates provide the exact same encryption strength as a $200 certificate. While some high-end “Extended Validation” certificates offer a financial warranty, the actual security of the data transmission is identical. For 99% of WooCommerce stores, a free Let’s Encrypt certificate is perfectly sufficient and meets all PCI compliance standards.

Conclusion

Securing your WordPress site isn’t just a technical requirement—it’s a commitment to your visitors’ safety and your brand’s reputation. Whether you are a small business owner in Santa Rosa CA or managing a high-traffic global blog, the steps to wordpress set ssl certificate are now more accessible than ever.

At wpOncall, we specialize in taking the stress out of WordPress security. We know that as a business owner, you don’t always have the time to troubleshoot mixed content errors or manage SSH commands. That’s why we offer proactive maintenance, daily backups, and unlimited support to ensure your site is always protected and performing at its best.

Our team is dedicated to fast response times and expert-level WordPress care. If you want to ensure your site stays secure without the headache, we invite you to secure your site with WordPress hosting and SSL through our managed services. Let us handle the technical heavy lifting so you can focus on growing your business.

it security audit services

Unmasking Vulnerabilities: The Essential Guide to Web Security Audits

Why IT Security Audit Services Are Essential for Every Business

IT security audit services are a formal, systematic way to verify that your security controls are implemented correctly, configured safely, and actually working to protect your digital assets. As threats evolve from basic malware to targeted ransomware and credential-based attacks, a surface-level check is no longer enough. A professional audit provides an independent, evidence-based view of your technical environment so you can prove your defenses match your risk. In the modern digital economy, where data is the most valuable currency, the ability to demonstrate a robust security posture is not just a technical requirement but a competitive advantage.

In 2024 and 2025, the threat landscape has shifted significantly. We are seeing a rise in AI-driven phishing attacks, sophisticated supply chain compromises, and the continued exploitation of legacy systems. For many businesses, the question is no longer if they will be targeted, but when. This reality makes the role of comprehensive auditing more critical than ever. An audit acts as a stress test for your organization, identifying where the cracks are before a malicious actor can exploit them. It moves your security strategy from a reactive “firefighting” mode to a proactive, risk-managed approach.

Here is a clear summary of what these services typically cover and why they matter:

What Why It Matters
Review of security policies and controls Confirms protections exist and are effective, ensuring written policies match real configurations.
Identification of vulnerabilities and gaps Finds misconfigurations, missing patches, and weak access points before attackers do.
Compliance verification (ISO 27001, HIPAA, PCI DSS, etc.) Reduces regulatory exposure and helps meet partner and customer requirements.
Documented evidence and audit reports Builds trust with clients and stakeholders by providing defensible verification of your security posture.
Remediation roadmap Provides a prioritized plan to fix issues and improve security maturity over time.

The business impact of a security failure can be severe. IBM’s Cost of a Data Breach Report 2024 reported the global average cost of a breach at $4.88 million. That number reflects far more than cleanup: downtime, incident response, legal costs, customer churn, and long-term reputation damage. For small and mid-sized businesses that depend on a website for leads, sales, and support, even a limited compromise (like injected malware or stolen admin credentials) can create immediate operational disruption. Furthermore, the indirect costs—such as the loss of intellectual property or the erosion of brand equity—can haunt a company for years after the initial incident is resolved.

A security audit is not just a compliance checkbox. It is a proactive defense strategy that helps leadership answer practical questions:

  • What are our highest-risk systems and accounts right now?
  • Which fixes reduce risk the fastest?
  • Can we show customers, partners, or insurers that our controls are real and repeatable?
  • Are we allocating our security budget to the areas that provide the most protection?

I’m Kevin Gallagher, founder of wpOncall. Over more than a decade managing hundreds of WordPress websites, I’ve seen how proper IT security audit services can be the difference between catching a vulnerability early and dealing with a full incident. In the sections below, you’ll see what audits cover, how they differ from assessments and penetration tests, and how to use the results to harden your environment. We will explore the technical nuances of modern auditing and provide a roadmap for businesses looking to secure their digital future.

It security audit services vocab to learn:

Understanding the Core of IT Security Audit Services

At its heart, an IT security audit answers one big question: “Are we as secure as we think we are, and can we prove it?” While many business owners assume a firewall or a basic security plugin is enough, professional it security audit services go much deeper. They provide a systematic evaluation of your entire digital infrastructure to ensure that your defenses are not only present but also correctly configured and actively monitored. This involves a deep dive into the “three pillars” of security: People, Processes, and Technology.

professional auditor reviewing server logs - it security audit services

A comprehensive audit examines several critical layers of your organization, ensuring that no stone is left unturned in the quest for digital resilience:

  • Asset Management: You cannot protect what you don’t know you have. Audits verify your inventory of hardware, software, and data assets. This process often uncovers “Shadow IT” – unauthorized applications or devices that create unmonitored security holes. In many cases, employees may use personal cloud storage or messaging apps for work purposes, inadvertently exposing sensitive company data to external risks. A thorough audit identifies these outliers and brings them under the umbrella of corporate security policy.
  • Access Controls: Auditors look for “ghost” accounts from former employees, verify that Multi-Factor Authentication (MFA) is enforced, and ensure the principle of least privilege is followed – meaning users only have the access necessary for their specific job functions. This is critical because credential theft remains one of the primary entry points for attackers. By strictly controlling who can access what, you significantly reduce the “blast radius” of a potential compromise.
  • Data Protection: Are your databases encrypted at rest? Is sensitive customer information sitting in plain text on a backup drive? Auditors check for encryption protocols (like TLS 1.3) and ensure data retention policies are being followed. They also evaluate the security of data in transit, ensuring that information moving between your servers and your users is shielded from interception.
  • Technical Safeguards: This involves checking firewalls, intrusion detection systems (IDS), network configurations, and endpoint protection to ensure a multi-layered defense system. Auditors look for “single points of failure” where a single misconfiguration could lead to a total system collapse.

We rely on the best practice guidelines outlined by CIS Center for Internet Security to perform a thorough security auditing process. These controls provide a prioritized set of actions that collectively form a defense-in-depth strategy. For those specifically using the world’s most popular CMS, you can explore More info about WordPress security audit services to see how these principles apply to WordPress architecture, which requires specialized knowledge of plugin vulnerabilities and theme security.

Defining Internal vs External Audits

Understanding the distinction between internal and external audits is vital for building a balanced security program. Both have their place, but they serve different strategic purposes.

Internal audits are conducted by your own IT team or internal security department. They are excellent for continuous improvement because your staff has deep company knowledge and understands the nuances of your specific workflows. Internal audits are often more frequent and can be used to monitor the progress of remediation efforts. However, they can suffer from “familiarity blindness” – where team members overlook risks because “that’s just how we’ve always done it,” or they may be hesitant to report issues that reflect poorly on their own department’s performance.

External audits provide an unbiased, third-party evaluation. These are often required for official certification requirements or to satisfy the security requirements of enterprise clients and insurance providers. An external auditor brings fresh eyes, specialized tools, and a broad perspective gained from working with many different organizations. They can issue official opinion letters that build significant trust with stakeholders, proving that your security claims are backed by independent verification.

The Scope of Modern Security Controls

Modern it security audit services cover a vast landscape that has expanded far beyond the traditional office network. Today’s audits must account for remote work, cloud-native applications, and mobile device management. Key areas include:

  1. Inventory Management: Tracking all devices and software to prevent unauthorized access. This includes IoT devices, which are often overlooked but can serve as entry points for attackers.
  2. Secure Configuration: Ensuring servers and network devices aren’t using default settings, which are often the first thing hackers exploit. See More info about common web server vulnerabilities to understand why default configurations are dangerous.
  3. Malware Defenses: Verifying that antivirus, EDR (Endpoint Detection and Response), and malware scanners are updated and scanning in real-time across all endpoints.
  4. Incident Response: Checking if you have a documented Incident Response Plan (IRP) and if your team has been trained to execute it. An audit will often include a review of past incidents to see how well the plan worked in practice.
  5. Security Awareness Training: Since humans are often the weakest link, auditors check if staff is regularly trained to spot phishing, vishing, and social engineering attacks. They look for evidence of a “security-first” culture within the organization.

Audit vs. Assessment: Navigating the Technical Landscape

Cybersecurity terms often get used interchangeably, but “audit,” “vulnerability assessment,” and “penetration test” are different tools for different outcomes. Choosing the wrong one can lead to a false sense of security or wasted resources. It is essential to understand the depth and intent of each service to ensure your security goals are met.

Feature IT Security Audit Penetration Test Vulnerability Assessment
Goal Verify control presence and adherence to requirements Demonstrate impact via simulated attack paths Identify known weaknesses that should be fixed
Method Evidence review + interviews + technical checks Manual testing by experts (often with custom tooling) Automated scanners and configuration checks
Scope Broad (Policies, People, Processes, Tech) Targeted (Specific apps, networks, or objectives) Mostly technical (systems, software, exposed services)
Deliverable Audit report mapped to controls/standards Exploit narrative, proof of concept, and remediation Prioritized list of findings (often CVE-based)
Frequency Annual or bi-annual Annual or after major changes Monthly or quarterly (continuous)

Many audits reference frameworks such as the NIST Cybersecurity Framework, which organizes security into six core functions: Govern, Identify, Protect, Detect, Respond, and Recover. This framework provides a common language for security professionals and business leaders to discuss risk. For web properties, you may also incorporate simulated attacks to validate whether findings are actually exploitable in a real-world scenario. This hybrid approach ensures that you aren’t just fixing theoretical problems, but addressing the most likely paths an attacker would take.

Cost Factors and Budgeting for Audits

Pricing for it security audit services varies depending on scope, number of systems, and compliance requirements. It is important to view these costs as an investment in risk mitigation rather than a simple expense. The cost of an audit is almost always a fraction of the cost of a data breach.

  • Small business / single site: Often $1,000 to $5,000 for a focused audit. This typically covers a technical review of the website, basic policy checks, and a vulnerability scan.
  • SMB / mid-market: Often $5,000 to $25,000, including policy review, infrastructure assessment, and perhaps a limited penetration test. This level of audit is suitable for companies with 20-100 employees and more complex data handling needs.
  • Enterprise or certification-driven audits: Full programs such as ISO 27001 or SOC 2 Type II can run $50,000 to $150,000+. These audits are highly rigorous, involving months of evidence collection and multiple rounds of testing.

Key cost drivers include complexity (cloud plus on-prem environments), evidence readiness (how organized your documentation is), depth of testing, and the commercial model (fixed-fee vs. time-and-materials). Investing in securing WordPress sites from hackers through structured auditing is typically far less expensive than incident response after a compromise. Furthermore, many cyber insurance providers now require proof of regular auditing to maintain coverage or to lower premiums.

Deliverables and Post-Audit Reporting

A strong audit delivers documentation useful to both executives and technical teams. The goal is to provide a clear path forward, not just a list of problems. A high-quality report should include:

  • Executive summary: Business-impact framing, top risks, and recommended priorities. This section is designed for non-technical stakeholders to understand the organization’s risk profile.
  • Technical findings: Detailed issues, severity ratings (Critical, High, Medium, Low), affected assets, and CVE (Common Vulnerabilities and Exposures) references where relevant.
  • Artifact collection: Evidence such as screenshots, log samples, and configuration exports that prove the findings are accurate.
  • Remediation roadmap: A prioritized plan with practical next steps, owners, and timelines. This helps the IT team manage their workload effectively.
  • Auditor opinion letter: A formal statement supporting due diligence with clients, partners, or insurers. This is often the most valuable piece for business development and compliance.

Think of this as a tailored version of an ultimate WordPress security guide for your environment: specific findings and fixes, not generic advice. The report should serve as a living document that guides your security improvements over the following year.

The Step-by-Step Process of Conducting an IT Security Audit

A professional audit follows a structured methodology to ensure consistency and thoroughness. By following a standardized process, auditors can ensure that no critical areas are missed and that the results are reproducible and defensible.

step-by-step audit workflow diagram - it security audit services

  1. Planning and Scoping: Define exactly what is being audited – your public-facing website, entire office network, or cloud storage. This prevents scope creep and keeps the project on budget. During this phase, the auditor will identify key stakeholders and establish the communication plan.
  2. Preparation Phase: Gather artifacts including documents, policies, network maps, and previous security reports. This is where the organization does the “heavy lifting” of organizing their data. See how we handle WordPress site audits for an example of web-focused preparation.
  3. Artifact Collection and Evidence Review: The auditor examines logs, interviews staff, and checks configurations against standards like ISO 27001 Compliance Requirements. They verify that policies are actually followed in practice, rather than just existing on paper. This often involves “walkthroughs” where the auditor observes a process being performed.
  4. Technical Testing: Hands-on scanning for vulnerabilities, checking firewall rules, and verifying encryption implementation. This phase confirms that technical reality matches written policy. It may include automated scans and manual configuration reviews of servers and network devices.
  5. Reporting Phase: Findings are compiled into detailed reports, including a draft for your team to review for factual accuracy and a final report for stakeholders. This phase includes a “closing meeting” where the auditor presents the key findings.
  6. Remediation and Follow-up: A good auditor offers a follow-up check (often 30-90 days later) to verify that issues are resolved and new controls are working. This ensures that the audit leads to actual security improvements, not just a report that sits on a shelf.

Preparing Your Organization for an Audit

Preparation is key to a smooth, cost-effective audit. An unprepared organization will spend more on auditor hours and likely receive a more critical report. Start by organizing documentation and performing a self-assessment. Use a WordPress security guide to check basics like two-factor authentication, plugin updates, and user role management.

Creating a central repository for security documentation—such as your IRP, employee handbook, and network diagrams—will save significant time during the evidence collection phase. You should also ensure that key personnel are available for interviews during the audit window. If your team is too busy to support the auditor, the process will drag on and costs will escalate.

Maintain a Risk Register that catalogs known threats and how you plan to handle them (Accept, Mitigate, Transfer, or Avoid). Having a Statement of Applicability (SoA) ready will make your auditor’s job easier and demonstrate security maturity. A Risk Register shows the auditor that you are already thinking about risk in a structured way, which builds confidence in your management processes.

How Frequently Should You Schedule IT Security Audit Services?

We recommend that organizations undergo it security audit services at least annually. This frequency ensures that you stay ahead of new threats and that your controls haven’t “drifted” over time. You should also trigger an audit if:

  • You undergo a major IT change, such as migrating to a new server or cloud infrastructure.
  • You work in a high-risk industry like healthcare, finance, or legal services where data sensitivity is paramount.
  • New regulations are passed that affect your business (e.g., changes to state privacy laws).
  • You have experienced a security incident or near miss, which indicates a potential failure in your current controls.
  • You are preparing for a merger or acquisition, where understanding the target’s security posture is essential for due diligence.

For many, website security for WordPress requires continuous monitoring and smaller quarterly reviews between formal annual audits to account for the rapid pace of plugin and theme updates.

Aligning with Global Standards: ISO, HIPAA, and Beyond

Compliance is a common driver for it security audit services. If you handle credit cards, health records, or personal data from regulated regions, you are auditing to reduce legal exposure and demonstrate repeatable controls. Compliance is not just about avoiding fines; it’s about meeting the baseline expectations of the global marketplace.

Common frameworks include:

  • ISO 27001: A widely recognized international standard for information security management systems (ISMS). It focuses on a risk-based approach to managing sensitive company information. See ISO 27001 Compliance Requirements.
  • SOC 2: Common for SaaS and service providers, centered on Trust Services Criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy. A SOC 2 report is often a prerequisite for doing business with enterprise-level clients. See SOC 2 Compliance and Framework Alignment.
  • HIPAA: For healthcare providers and their business associates, focused on safeguarding Protected Health Information (PHI). HIPAA audits are essential for avoiding massive OCR fines. See HIPAA Compliance Requirements.
  • GDPR: For organizations serving EU residents, requiring appropriate security of personal data and strict reporting of breaches. GDPR has set the standard for privacy laws globally. See GDPR Compliance Requirements.
  • PCI DSS: For organizations processing, storing, or transmitting cardholder data. This is a contractual requirement from the major card brands. See PCI DSS Compliance Requirements.

A well-run audit maps findings back to applicable controls so you can reuse work across requirements. For example, a control that satisfies ISO 27001 may also satisfy parts of SOC 2 or HIPAA. For WordPress site owners, a WordPress security audit complete guide helps translate these high-level compliance expectations into concrete settings, such as database prefix changes, file permission hardening, and secure API configurations.

Supporting Federal and Industry-Specific Frameworks

Some organizations must align with additional frameworks depending on their sector or the type of government data they handle:

  • NIST SP 800-53: A comprehensive catalog of security and privacy controls for federal information systems and organizations. It is often the “gold standard” for high-security environments. See NIST SP 800 53.
  • HITRUST CSF: A certifiable framework that leverages various standards (ISO, NIST, HIPAA, PCI) to provide a comprehensive security and privacy roadmap for the healthcare industry. See HITRUST CSF certification.
  • OWASP Top 10: While not a formal compliance standard, these practical web application risks heavily influence audit scope for any business with a web presence. See OWASP Top 10.

There are also legal expectations around accessibility that are increasingly being folded into broader IT audits. The US government maintains website accessibility guidelines and the IRS provides an ADA Tax Credit for eligible improvements. Ensuring your site is accessible is not just a legal requirement but also expands your reach to all potential users.

Choosing the Right Provider for IT Security Audit Services

Look for credentials, relevant experience, and a methodology that produces actionable findings. The quality of your audit is directly tied to the expertise of the auditor. Key certifications to look for include:

  • CISA (Certified Information Systems Auditor): The premier audit-focused credential, emphasizing the ability to assess vulnerabilities and report on compliance. See CISA Experience and Strengths.
  • CISSP (Certified Information Systems Security Professional): A broad security leadership credential that ensures the auditor understands the entire security ecosystem. See CISSP Experience and Strengths.
  • OSCP / OSWE: These are hands-on testing skills that indicate the auditor can perform deep technical validation. See OSCP Experience and Strengths and OSWE Experience and Strengths.
  • Framework-specific capability: Confirm the team has direct experience with your required standard. A directory is available at framework specific credentials.

Before signing a contract, ask for a clear scope statement, sample reports with specific findings, a description of how they handle sensitive evidence, and a plan for follow-up verification. A good provider will be transparent about their process and willing to tailor their approach to your specific business needs.

Identifying Common Gaps and Strengthening Your Defenses

Certain patterns emerge consistently across audits, regardless of the industry. These are the most frequent gaps that it security audit services uncover, and they often represent the “low-hanging fruit” for attackers:

  1. Weak or Reused Passwords: Still the number one way hackers gain access. Despite years of warnings, many users still use simple passwords or reuse the same password across multiple sites. Implementing a robust password policy and MFA (Multi-Factor Authentication) is the first and most effective remediation step.
  2. Outdated and Unpatched Software: Unpatched plugins, themes, or server software are like leaving your front door open. Automated bots constantly scan the internet for known vulnerabilities. An audit often finds systems that haven’t been updated in months or even years.
  3. Missing or Broken Encryption: Data sent over insecure HTTP or sensitive files stored unencrypted represent major risk. Auditors check for valid SSL/TLS certificates and proper database encryption. They also look for “encryption in use” gaps where data is exposed during processing.
  4. Lack of Employee Training: Phishing emails remain a leading cause of ransomware. Without regular simulations and training, employees are likely to fall for increasingly sophisticated social engineering tactics.
  5. Misconfigured Cloud Storage: Leaving sensitive files on public cloud buckets (like AWS S3) is a common and devastating mistake. Auditors use specialized tools to find these exposed assets before they are discovered by malicious actors.
  6. Inadequate Logging and Monitoring: Many organizations have no idea they’ve been breached because they aren’t looking at their logs. An audit will verify that logs are being collected, protected from tampering, and actively reviewed for suspicious activity.

By identifying these issues in a WordPress site security review, you can stop a breach before it starts. The goal is to create a “hostile environment” for attackers, where every step they take is difficult and likely to be detected.

Remediation and Continuous Improvement

Once the report is in your hands, the real work begins. Perform a Root Cause Analysis (RCA) for every major finding. If the audit found outdated software, don’t just patch it – ask why it wasn’t patched automatically. Was it a lack of tools, a lack of time, or a fear of breaking the site? Addressing the root cause leads to better policies and more reliable systems.

Many organizations are moving toward Zero-Trust Architecture, where no user or device is trusted by default, even if they are inside the corporate network. This approach requires continuous verification of identity and device health. Implementing tools like SIEM (Security Information and Event Management) helps aggregate logs from across your infrastructure and spot threats in real-time using AI and machine learning. For WordPress users, it security audit services often result in better firewall configurations, stricter access hierarchies, and more robust backup strategies that include off-site storage and regular restoration testing.

The Role of Automation in Modern Auditing

Modern auditing uses a hybrid methodology combining automation with human expertise. AI-driven tools can scan millions of lines of code in seconds, finding known vulnerabilities and configuration errors quickly. This allows auditors to cover more ground in less time. However, manual verification remains essential – automated tools may flag false positives or miss complex logic flaws that require human intuition to understand. This hybrid approach ensures data integrity and provides real-world attack simulations that automated tools cannot match. The human auditor provides the context, while the automation provides the scale.

Frequently Asked Questions about IT Security Audit Services

What is the average cost of an IT security audit?

As mentioned previously, the cost varies based on scope. For a small business or a single high-traffic website, expect to pay between $1,000 and $5,000 for a focused, high-quality audit. For mid-sized organizations needing compliance certifications like SOC 2, the cost typically ranges from $20,000 to $50,000. Large enterprises with complex, global infrastructures can see costs exceeding $100,000 for a full-scale audit. Factors such as the number of endpoints, the complexity of the cloud environment, and the specific regulatory requirements all play a role in determining the final price.

How long does a typical security audit take to complete?

A focused audit of a single website or a small office network can usually be completed in 3 to 5 business days. However, a full-scale enterprise audit for something like ISO 27001 or HIPAA compliance can take several weeks or even months. This time is spent on data collection, staff interviews, technical testing, and the final reporting process. The “readiness” of the organization—how quickly they can provide requested evidence—is the biggest variable in the timeline.

What is the difference between a security audit and a penetration test?

An audit is a comprehensive, high-level review of your policies, people, and technical controls to ensure you are meeting a specific standard or framework. It is about verification and compliance. A penetration test is a specific, technical exercise where a “white hat” hacker tries to actively break into your systems to find exploitable holes. Think of an audit as checking if the door is locked and the alarm is set, while a penetration test is trying to pick the lock. Both are valuable, but they serve different purposes in a security program.

Will a security audit disrupt my business operations?

A professional audit is designed to be as non-intrusive as possible. Most of the work involves reviewing documentation and logs. Technical scanning is usually performed during off-peak hours to ensure there is no impact on website performance or employee productivity. Your auditor should work closely with your IT team to schedule any tests that might carry a risk of disruption, such as vulnerability scans on legacy systems.

What happens if the audit finds major security holes?

Finding gaps is actually the goal of the audit! It is much better for a friendly auditor to find a hole than for a malicious hacker to find it. Your audit report will include a prioritized remediation plan. You should work through the “Critical” and “High” risk items first. A good audit firm will provide guidance on how to fix these issues and may offer a follow-up review to confirm the fixes were successful. This process is about improvement, not punishment.

Can an audit help me get cyber insurance?

Yes, absolutely. Most cyber insurance providers now require a detailed assessment or audit of your security controls before they will issue a policy. Having a recent, professional audit report can not only help you secure coverage but may also lead to lower premiums by demonstrating that you are a “lower risk” client. Insurers want to see that you have MFA, regular backups, and a documented incident response plan in place.

How do I choose between an internal and external audit?

If you are looking for continuous improvement and have a capable IT team, internal audits are a great starting point. However, if you need to satisfy external stakeholders (clients, regulators, insurers) or want an unbiased perspective, an external audit is necessary. Many organizations use a “hybrid” approach, performing internal audits quarterly and an external audit annually.

Conclusion

Navigating the world of it security audit services can feel overwhelming, especially with the constant stream of news about new data breaches and evolving cyber threats. However, a professional audit is the single best investment you can make in your business’s long-term longevity and digital health. It moves you away from the “hope for the best” strategy and gives you a data-driven, actionable plan for protecting your most valuable assets. In an era where trust is hard to earn and easy to lose, being able to prove your security posture is a powerful business enabler.

At wpOncall, we specialize in taking the complexity out of this process, particularly for WordPress users who face unique security challenges. We provide the deep technical expertise needed to ensure your site isn’t just “running,” but is actively defended against the modern threat landscape. Our approach combines rigorous technical testing with a deep understanding of business risk, ensuring that your security strategy supports your growth rather than hindering it. We understand that for many businesses, the website is the front door to their brand, and keeping that door secure is our top priority.

From our base in Santa Rosa, CA, we help businesses across the country with daily updates, remote maintenance, and manual backup tests that go far beyond what a simple plugin can offer. We don’t just find problems; we optimize your site to prevent them from happening in the first place. We believe that security should be a foundation, not an afterthought. Our team stays at the forefront of the latest security trends, ensuring that our clients are protected against both known and emerging threats.

If you are ready to stop guessing about your security and start knowing exactly where you stand, it is time for a professional review. A comprehensive audit provides the peace of mind that comes from knowing your defenses have been tested and verified by experts. Check out our extensive resources on WordPress Site Security or reach out to us today to see how we can help you build a more resilient, secure, and successful digital future. Your data, your reputation, and your peace of mind are worth the investment. Let us help you turn security from a source of anxiety into a source of strength.

WordPress incident response

The Emergency Guide to Website Malware Removal

What to Do When Your WordPress Site Gets Hacked

WordPress incident response is the specialized process of detecting, containing, and recovering from a security breach on your WordPress website. In the world of cybersecurity, an incident is any event that violates an organization’s security policies or standard operating procedures. For a WordPress site owner, this usually manifests as a malware infection, a database injection, or an unauthorized administrative takeover. If your site has been compromised, the speed and structure of your response will determine whether you lose a few hours of traffic or your entire business reputation. Here are the immediate, non-negotiable steps to take:

  1. Block public access – Put your site in maintenance mode or restrict access via .htaccess to prevent further infection of visitors.
  2. Change all passwords – This includes WordPress admin accounts, hosting panel access, SFTP, SSH, and database credentials.
  3. Preserve evidence – Take screenshots and create a full forensic backup of the infected site before you begin the cleanup process.
  4. Scan for malware – Use an external scanner like Sucuri SiteCheck to assess the visible damage and identify malicious redirects.
  5. Contact your host – Your hosting provider may have server-level logs or off-site backups that are critical for identifying the attack vector.
  6. Clean and restore – Remove malicious code, replace core files with fresh versions, and sanitize your database tables.
  7. Harden and monitor – Patch the original vulnerability and set up ongoing monitoring to prevent the “reinfection loop.”

Finding out your WordPress site has been hacked is a gut-punch moment that triggers immediate panic. Your business may be losing sales every minute the site is down, or worse, serving malware to your loyal visitors. Your search engine rankings could be dropping as Google flags your site with a “This site may be hacked” warning, which can take weeks to clear. And somewhere in the background, an automated botnet is likely still probing your server for the next opening.

As former Cisco Chairman John Chambers once famously said, “There are two types of companies: those that have been hacked, and those who don’t know they have been hacked.” That quote hits differently when it’s your site, your data, and your customers on the line. The reality of modern web security is that WordPress, powering over 40% of the internet, is a massive target for automated scripts. These scripts don’t care about your content; they want your server’s processing power to send spam, host phishing pages, or mine cryptocurrency.

The good news? A fast, structured response limits the damage significantly. Most WordPress hacks are not targeted attacks against you personally. They are automated exploits scanning thousands of sites at once, looking for unpatched plugins, weak passwords, or misconfigured servers. That means the same disciplined response plan works in almost every case. By following a professional WordPress incident response framework, you can move from a state of crisis to a state of recovery in a matter of hours.

This guide walks you through every phase of the response lifecycle – from the first moment you suspect something is wrong, all the way through deep-tissue cleanup, recovery, and long-term hardening. I’m Kevin Gallagher, founder of wpONcall, and over more than a decade managing hundreds of WordPress websites, I’ve handled incident response scenarios ranging from simple malware injections to complex backdoor attacks that took days to fully unravel. Everything in this guide comes from real-world experience cleaning up hacked sites and helping business owners get back online fast.

WordPress incident response terms explained:

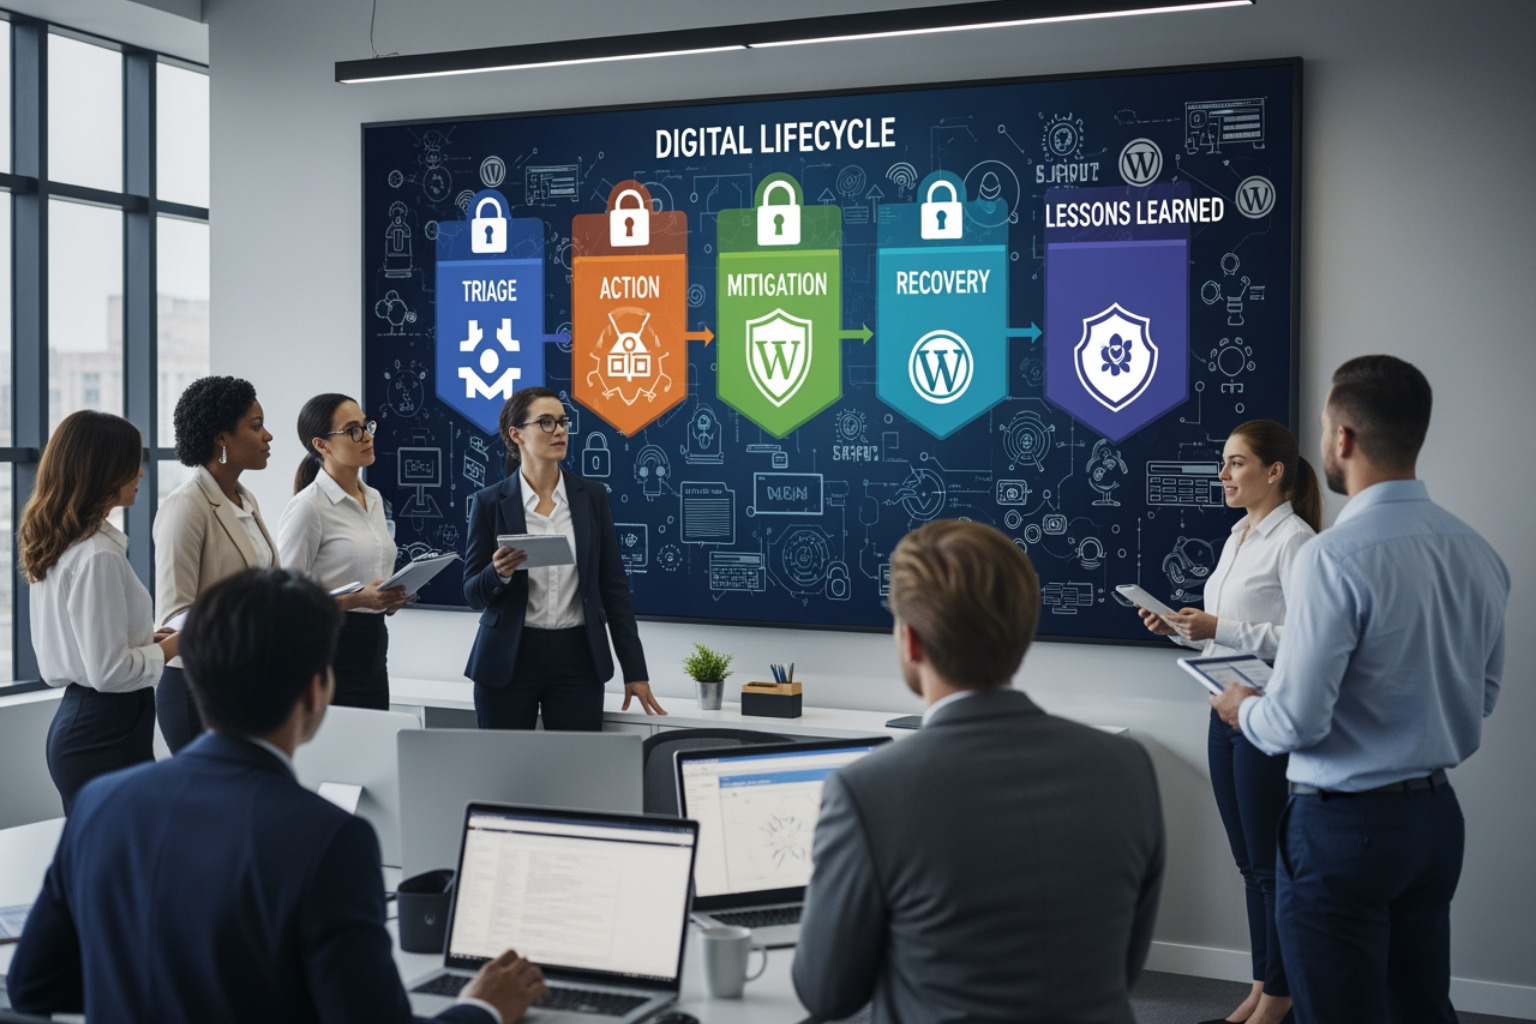
The 5 Phases of a WordPress Incident Response Plan

The WordPress incident response lifecycle showing triage, action, mitigation, recovery, and lessons learned - WordPress

When a breach occurs, panic is your worst enemy. To move from chaos to control, we follow a structured lifecycle modeled after the NIST (National Institute of Standards and Technology) guidelines for computer security incident handling. This isn’t just about deleting a few bad files; it’s about ensuring the attacker doesn’t have a “spare key” to get back in ten minutes later. A common mistake site owners make is deleting the malware but leaving the backdoor, leading to a cycle of reinfection that can destroy a site’s SEO permanently.

An effective WordPress incident response plan consists of five distinct, chronological phases:

  1. Triage: This is the “stop the bleeding” phase. We identify the breach, block the attacker’s access, and preserve evidence. During triage, we determine the scope of the incident: Is it just one site, or is the entire server compromised? We also implement immediate containment measures to prevent the malware from spreading to other users or sites on the same hosting account.
  2. Action: Here, we perform deep scans and manual audits to find every trace of malicious code. This involves looking beyond the obvious. We check the database for rogue admin users, audit the wp-content/uploads directory for executable scripts, and examine the theme’s functions.php for hidden backdoors. This is the most labor-intensive part of the process.
  3. Mitigation: We close the vulnerability that allowed the hack in the first place. If the entry point was an outdated plugin, we update or replace it. If it was a compromised password, we implement a site-wide password reset and enforce Two-Factor Authentication (2FA). Without mitigation, the cleanup is temporary.
  4. Recovery: This involves restoring clean files, verifying site integrity, and requesting removal from search engine blocklists. We move the site from a “quarantine” environment back to production, ensuring that all functionality is restored and that the site is no longer flagged as dangerous by browsers or security software.
  5. Lessons Learned: We document the attack vector and update our WordPress disaster recovery plan to ensure it never happens again. This “post-mortem” analysis is vital for long-term security. We ask: How did they get in? Why wasn’t it detected sooner? What tools do we need to prevent this in the future?

Statistics show that attackers typically exploit vulnerabilities massively using automated tools. They don’t care if you’re a small local business in Santa Rosa or a global enterprise; they just want your server resources. For mission-critical sites, a 1-hour response time is the industry gold standard, with full remediation ideally occurring within 24 hours to minimize financial and reputational fallout. The longer a site remains infected, the higher the “dwell time,” which increases the likelihood of being blacklisted by Google.

Why Every Site Owner Needs a WordPress Incident Response Strategy

Relying on “luck” is not a security posture. Without a predefined strategy, you risk permanent data loss and severe SEO impact. When Google flags your site, your organic traffic can drop to zero instantly, and regaining that trust can take months. A proactive strategy provides operational certainty. It ensures that when—not if—an automated botnet finds a hole in your defenses, you have a playbook ready to execute. This involves regular site maintenance, off-site backups, and working with security experts who understand the nuances of the WordPress ecosystem. A well-documented plan reduces the “Time to Recovery” (TTR), which is the most critical metric in incident management.

Immediate Triage: Containing the Breach and Preserving Evidence

Server access logs being reviewed for suspicious IP addresses and unauthorized entry points - WordPress incident response

The moment you realize your site is compromised, your first priority is containment. You need to prevent the malware from spreading to your visitors and stop the attacker from further modifying your data. This is the “Golden Hour” of WordPress incident response. If you act quickly, you can prevent the search engines from indexing the malicious content, which saves you from the dreaded “This site may be hacked” warning.

Step 0: Block Access. If you can still access your dashboard, use a maintenance mode plugin to show a static page to visitors. If you’re locked out, use your hosting panel or edit your .htaccess file to allow only your specific IP address. This “whitelisting” approach effectively freezes the site for everyone else while you work. A sample .htaccess rule for this would be: order deny,allow deny from all allow from [YOUR_IP_ADDRESS]

Step 1: Preserve Forensics. Before you start deleting files, create a forensic snapshot. This is a read-only copy of the entire site as it exists in its infected state. Why? Because you need to understand how they got in. If you delete the evidence, you might miss the backdoor they left behind. Document everything: take screenshots of defaced pages, note the timestamps of when you first noticed issues, and save any weird error messages. This documentation is vital when fixing broken WordPress sites because it helps identify the timeline of the breach. Check your server’s access.log and error.log files; they often contain the IP address of the attacker and the specific file they exploited.

Critical Password Rotation and Access Control

Once the site is isolated, you must change every single password associated with the account. Do this in a specific order to ensure the attacker doesn’t use one compromised credential to reset another. Hackers often leave “sleeper” accounts in the database, so simply changing your own password isn’t enough. You must audit the entire user list.

  1. Hosting Control Panel: If they have this, they own the server, the email, and the backups.
  2. SFTP/SSH: This is how files are moved. Ensure no unauthorized SSH keys have been added to the authorized_keys file.
  3. Database Credentials: Found in your wp-config.php. After changing the password in the hosting panel, you must update the file.
  4. WordPress Admin Users: Check the Users list for any rogue accounts. Delete any account you didn’t create, especially those with Administrator privileges.

Use a password manager like 1Password or LastPass to generate complex, unique strings of at least 16 characters. To truly kick the attacker out, you must also terminate all active sessions. The easiest way to do this is by regenerating your secret keys (salts) using the WordPress key generator and pasting them into your wp-config.php file. This forces everyone—including the hacker—to log in again. This is a key step in preventing future WordPress hacks.

When to Contact Your Hosting Provider

Your host is your partner in this. If your account has been suspended, they likely detected malicious traffic or resource spikes. Reach out and ask for:

  • Server Logs: These can show exactly which file was accessed and from which IP. Look for POST requests to unusual PHP files.
  • IP Allowlisting: If they’ve blocked your site, ask them to allow your IP so you can perform the cleanup.
  • Backup Availability: They might have a clean version of your site from 48 hours ago. Ask for the retention policy of their backups.
  • Server-Side Scanning: Many hosts offer tools like ClamAV that can find malware signatures that frontend scanners miss. Reviewing WordPress error logs can also reveal the “chatter” of a failing script or a malicious injection. If you are on a shared hosting environment, ask if other sites on the server have been affected, as cross-site contamination is a common issue.

Forensic Analysis and Malware Eradication Strategies

Now we go hunting. Malware in WordPress often hides in plain sight, using names that look like core files (e.g., wp-log-php instead of wp-login.php). Common “Indicators of Compromise” (IoC) include site defacement (the obvious “Hacked by…” message), sneaky redirects to suspicious domains, pharma hacks (where your site suddenly sells discount medications in search results), and SEO spam that injects thousands of junk links into your footers or hidden div tags.

Start with a frontend scan using Sucuri SiteCheck. It’s a great way to see what the public (and Google) sees. Next, check your URL against VirusTotal to see which blocklist authorities have already flagged you. For the backend, if your host allows it, run a ClamAV Server-Side Scanner to check the actual file contents against known malware signatures. You can see more about what a hacked WordPress site looks like to help identify these symptoms. Remember that some malware is “environment-aware” and will only show itself to mobile users or search engine bots, making it invisible to you in a standard desktop browser.

Manual File Auditing and Integrity Monitoring

Automated scanners are good, but they aren’t perfect. Skilled hackers write code specifically designed to bypass them using obfuscation techniques like Base64 encoding or string reversal. You must manually audit critical files for suspicious functions like eval(), base64_decode(), gzinflate(), or str_rot13(). While these functions have legitimate uses, they are the hallmarks of obfuscated malware when found in core files.

  • wp-config.php: Look for extra code at the very top, before the <?php tag. This is a common place for hackers to include a global backdoor.
  • index.php: This is a favorite spot for redirects. Check both the root index.php and the one in your theme folder.
  • functions.php: Hackers often hide backdoors here because it loads on every page. Look for code that creates new users or sends emails.
  • .htaccess: Check for rules that redirect mobile users or search engine bots. Hackers use this to steal your traffic without you noticing.

A pro tip is to use the WP-CLI verify-checksums command. This compares your core WordPress files against the official versions in the repository. If a file has even one extra character, this tool will flag it. This is an essential part of debugging in WordPress. If the checksums don’t match, you know exactly which files have been tampered with.

Auditing Plugins and Themes for Backdoors

Most hacks enter through a vulnerable plugin or theme. If you’ve used “nulled” (pirated) plugins, there is a 99% chance they contain a backdoor. Even legitimate plugins can be exploited if they aren’t updated. During your audit, delete any plugin or theme you aren’t actively using. For the ones you keep, don’t just “update” them—delete the folder entirely via SFTP and reinstall a fresh copy from the official WordPress.org repository or the developer’s site.

Check your /wp-content/uploads/ directory; there should never be a .php file in there. This directory is meant for media files like JPEGs and PNGs. If you find a PHP file here, it’s almost certainly a web shell that allows the attacker to execute commands on your server. A thorough WordPress security audit is the only way to be sure you’ve cleared the path and identified the original entry point.

Database Sanitization and Core File Restoration

The database is often overlooked during a cleanup, but it’s where “Pharma hacks” and rogue admin users live. If you clean the files but leave the database infected, the site will remain compromised. Hackers often use the wp_options table to store malicious scripts that execute every time a page loads, or they use the wp_posts table to inject thousands of spam links that are hidden from regular users but visible to search engine crawlers.

Use a tool like Adminer or phpMyAdmin to run SQL queries. You are looking for:

  • Rogue Admins: Run SELECT * FROM wp_users; to see if there are any accounts you don’t recognize. Pay close attention to the user_registered date.
  • Spam Content: Search the wp_posts table for keywords related to the hack (e.g., “viagra”, “casino”, “luxury watches”).
  • Malicious Options: Check wp_options for large, serialized strings that don’t belong to your known plugins. Look for options like default_role being changed to administrator.
Feature Manual Cleaning Full Restoration
Precision High – keeps all recent data Low – loses data since last backup
Speed Slow – requires deep auditing Fast – overwrites everything
Risk High – might miss a hidden backdoor Low – if the backup is truly clean
Best For Sites with high-frequency content Sites that haven’t changed recently

Cleaning the database is a core part of our WordPress malware removal process. If you find malicious code in the database, you must be careful when deleting it, as serialized data can break your site if edited incorrectly.

Safe Core File Replacement and Verification

The safest way to ensure your core files are clean is to replace them entirely. This is a standard procedure in WordPress incident response because it removes any doubt about file integrity.

  1. Download a fresh copy of WordPress from WordPress.org.
  2. Delete your /wp-admin/ and /wp-includes/ directories entirely. Do not just overwrite them.
  3. Upload the fresh versions from your download.
  4. Replace all files in the root directory except wp-config.php and .htaccess (which you should have already audited).

This ensures that any “zombie” code hidden in the core files is wiped out. Always perform this in a staging environment first to ensure nothing breaks before you restore your website from backup to production. Once the core is clean, repeat the process for your plugins and themes.

SEO Recovery and Blocklist Removal

Once the site is clean, you have to tell the world. If you were blacklisted, your search traffic won’t return until you request a review. Log into Google Search Console and Bing Webmaster Tools. Check the “Security Issues” tab. Once you’ve verified the site is clean, click the “Request Review” button. Be honest: tell them what happened, the vulnerability you found, and the specific steps you took to fix it. This is the final step in a complete WordPress site recovery. If you were dealing with a WordPress redirect hack, ensure those redirects are completely gone by testing your site from different IP addresses and devices before requesting the review.

When to Hire Professional WordPress Incident Response Services

There are times when DIY isn’t enough. If you find yourself in a “reinfection loop”—where you clean the site and it’s hacked again 24 hours later—you have a hidden backdoor or a server-level vulnerability that requires professional tools. Professional WordPress malware removal services are essential when:

  • The site handles sensitive customer data, PII, or credit cards.
  • The hack is complex (e.g., cross-site contamination on a shared server).
  • You simply don’t have the 10-20 hours required for a deep forensic audit.
  • You need a guaranteed 1-hour response and 24-hour resolution to keep your business running. Experts have access to proprietary databases of malware signatures that aren’t available to the public.

Conclusion

Recovering from a hack is a marathon, not a sprint. Once the immediate fire is out, you need a 30/60/90-day hardening plan to ensure it never happens again. Security is a process, not a product. The goal of WordPress incident response is not just to fix the current problem, but to build a more resilient infrastructure for the future. This includes:

  • Immediate: Enable Two-Factor Authentication (2FA) for all users and implement a Web Application Firewall (WAF).
  • 30 Days: Disable XML-RPC if you don’t use the mobile app, and implement login protection to throttle brute-force attacks. Audit all user permissions.
  • 60 Days: Set up file integrity monitoring and verify your WordPress backup services are running daily and stored offsite in a secure cloud environment.
  • 90 Days: Conduct a full security review of all third-party integrations, API keys, and connected services. Ensure your hosting environment is running the latest version of PHP.

At wpOncall, we specialize in this exact type of proactive maintenance and emergency response. We don’t just clean the mess; we tighten the ship so the “hacker-pirates” move on to an easier target. Based right here in Santa Rosa, CA, we understand that for a local business, your website is your digital storefront. Don’t leave it unlocked. A single breach can cost thousands in lost revenue and recovery fees, making proactive security the most cost-effective investment you can make.

Frequently Asked Questions about WordPress Incident Response

How do I know if my WordPress site has been hacked?

Common signs include unexpected redirects to other sites, new administrator users you didn’t create, strange pop-ups or “pharma” ads, and warnings from Google or your hosting provider. Sometimes, the only sign is a sudden, unexplained drop in site performance or search rankings. You might also notice your server’s CPU usage spiking as it’s used for malicious tasks.

Can I clean a hacked WordPress site myself?

Yes, if you have technical experience with SFTP, SQL, and the WordPress file structure. However, hackers are experts at hiding backdoors in obscure locations. If you miss just one line of code, the attacker can regain access instantly. For business-critical sites, professional help is usually the safer and faster route.

How long does it take to recover from a WordPress hack?

A basic cleanup can take 2 to 4 hours, but a full forensic recovery—including database sanitization, file integrity verification, and blocklist removal—typically takes 24 to 48 hours. The speed of recovery depends heavily on whether you have a recent, clean backup available and how quickly you detected the breach.

Will my SEO recover after a hack?

Yes, but it takes time. Once you’ve cleaned the site and Google has processed your “Request Review,” the warnings will be removed. However, if the hack resulted in thousands of spam pages being indexed, it may take several weeks for those to drop out of the search results. Consistent, clean content and a secure site will eventually restore your rankings.

What is the most common way WordPress sites get hacked?

Over 90% of WordPress hacks are due to vulnerabilities in plugins and themes, followed by weak passwords and insecure hosting environments. Using outdated software is the equivalent of leaving your front door wide open. Regular updates and a strong firewall are your best lines of defense.

Learn more about WordPress site security and how to stay protected.

New Security Release: 4.2.4

Today, WordPress 4.2.4 was released as an important security fix. This update comes just one week after the release of WordPress 4.2.3.

4.2.3 caused quite a few issues with many sites as it changed the way WordPress uses shortcodes. This caused many sites to break their formatting when they relied of shortcodes to display content. The release team did not give a lot of warning to this change, although it was important to close the security hole with cross-site scripting.

This update, 4.2.4 supposedly fixed the issue sites were having with 4.2.3, so many plugin and theme authors will be happy. This update also addresses more issues with cross-site scripting as well as a SQL injection vulnerability.

You should update your site right away and always remember to backup your site before updating!

Read more here: http://wordpress.org/news/2015/08/wordpress-4-2-4-security-and-maintenance-release/

Important WordPress Security Release Today: 4.2.3

WordPress 4.2.3 was released today as an important security patch. There will not be any visual changes in this update (as with all other incremental WordPress updates), but it is extremely important to update to secure your site.

Specifically, the update addresses:

a cross-site scripting vulnerability, which could allow users with the Contributor or Author role to compromise a site.

Read more about it here.

All wpONcall members are already updated. Have you updated yet?